operate
Security Header Audit
Every security header on your live URL, graded — HSTS, CSP, cookie flags, WAF fingerprint.
What you get
Every header, graded
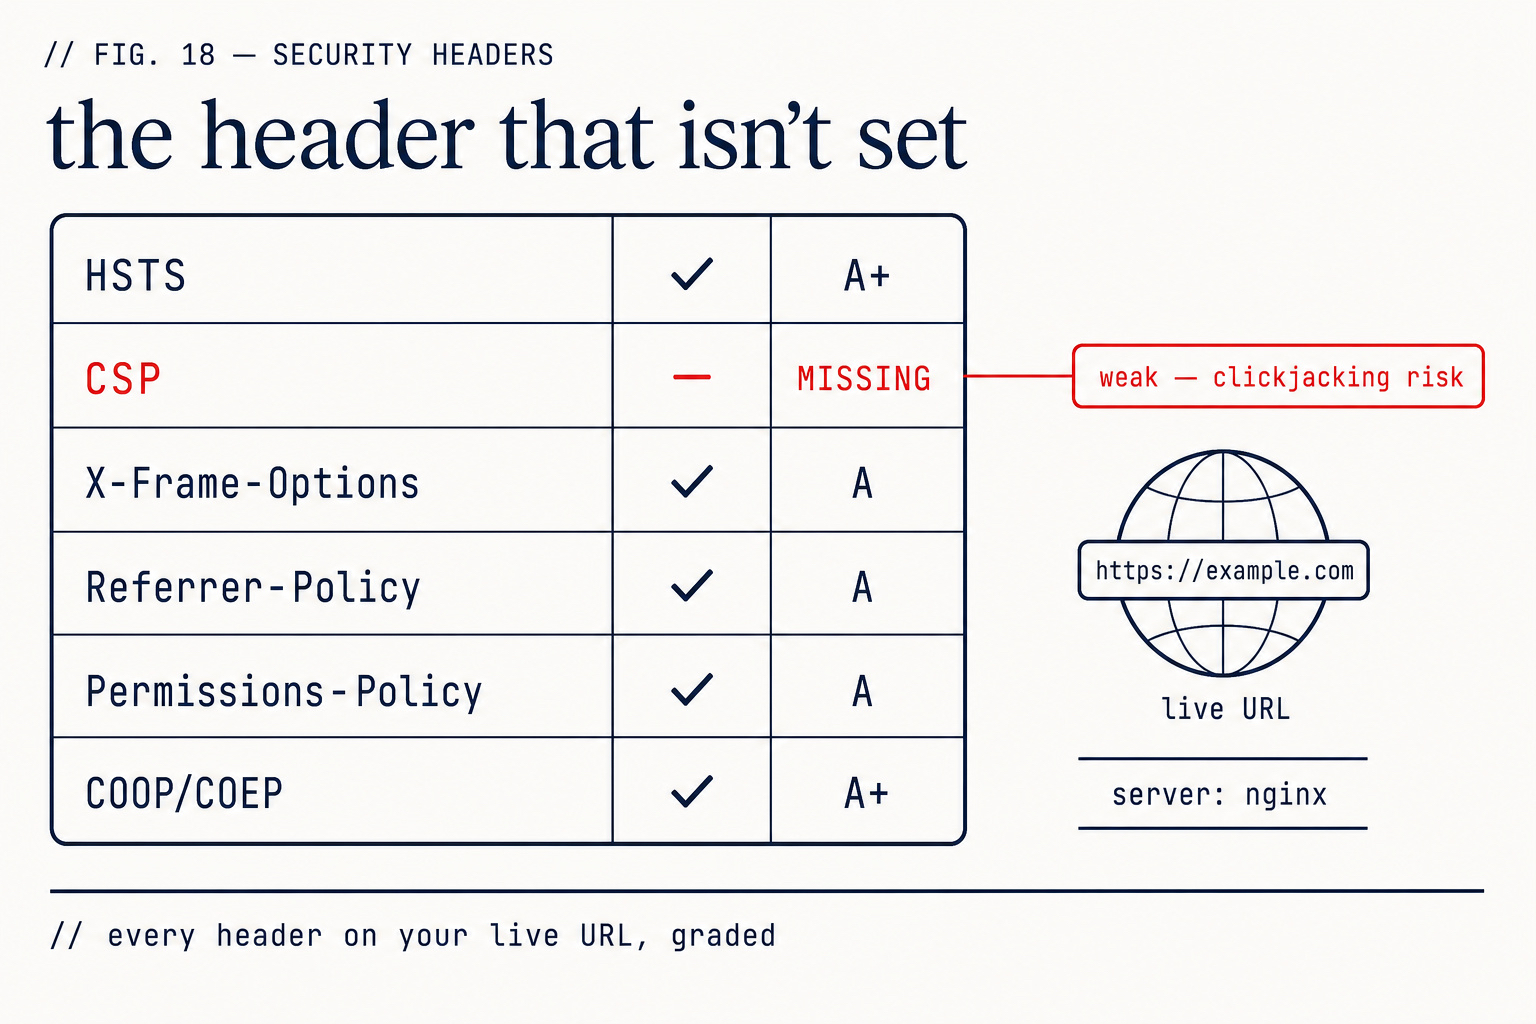
HSTS, CSP quality, clickjacking protections, cookie flags, Referrer- and Permissions-Policy, COOP/COEP — every security header on your deployed URL is checked and graded.
Fingerprint and disclosure
ZipLoom also flags server and framework disclosure and fingerprints your WAF/CDN, so you see what an attacker sees.
Cookie flags and downgrade paths
Beyond CSP and HSTS, the audit checks that session cookies carry Secure, HttpOnly, and SameSite, and that no plaintext path lets an attacker downgrade the connection. A missing HttpOnly flag turns any XSS into session theft.
How the header audit works
- 1
ZipLoom requests your live URL after deploy.
- 2
It reads and grades every security-relevant response header.
- 3
Weak or missing headers are surfaced against best practice.
What this check inspects
Content-Security-Policy — present, and whether it's permissive enough to be decorative.
HSTS, so browsers refuse to talk to your domain over plaintext.
Session cookie flags: Secure, HttpOnly, and SameSite.
X-Frame-Options / frame-ancestors, X-Content-Type-Options, and Referrer-Policy.
What it means when this fails
Missing headers rarely cause an incident on their own; they remove the guardrails that keep a small bug small. Without HttpOnly, any cross-site scripting bug becomes session theft. Without frame protection, your authenticated UI can be framed and clicked by a site you don't control.
Questions
- Aren't these set by my host automatically?
- Some are, most aren't, and the defaults differ by platform. The audit reports what your live response actually carries rather than what the platform's documentation says.
- Will a strict CSP break my app?
- It can, which is why the report tells you what your page currently loads so you can write a policy that fits rather than pasting a strict one and hunting breakages.
- Do headers matter for an API?
- Yes — cookie flags, CORS, and content-type protections apply to API responses too.
What it replaces
Checkly Starter
Synthetic API and Playwright browser checks. Team plan $64/mo for all regions.
Better Stack Uptime
Uptime monitoring, on-call and status pages. Tells you it broke; doesn't roll the release back.
Snyk Team
Per contributing developer, 5-seat minimum (~$1,500/yr entry). Code + dependency scanning; does not deploy your app.
ZipLoom Solo — all 28 features included
Deploy, security scan, and monitoring in one flat price. Guild $40/mo · Studio $70/mo · Business $299/mo.
Related features