security
Compliance Readiness Mapping
SOC 2, HIPAA, and GDPR controls mapped to your deploy — with a PDF export.
What you get
Three frameworks, mapped to your deploy
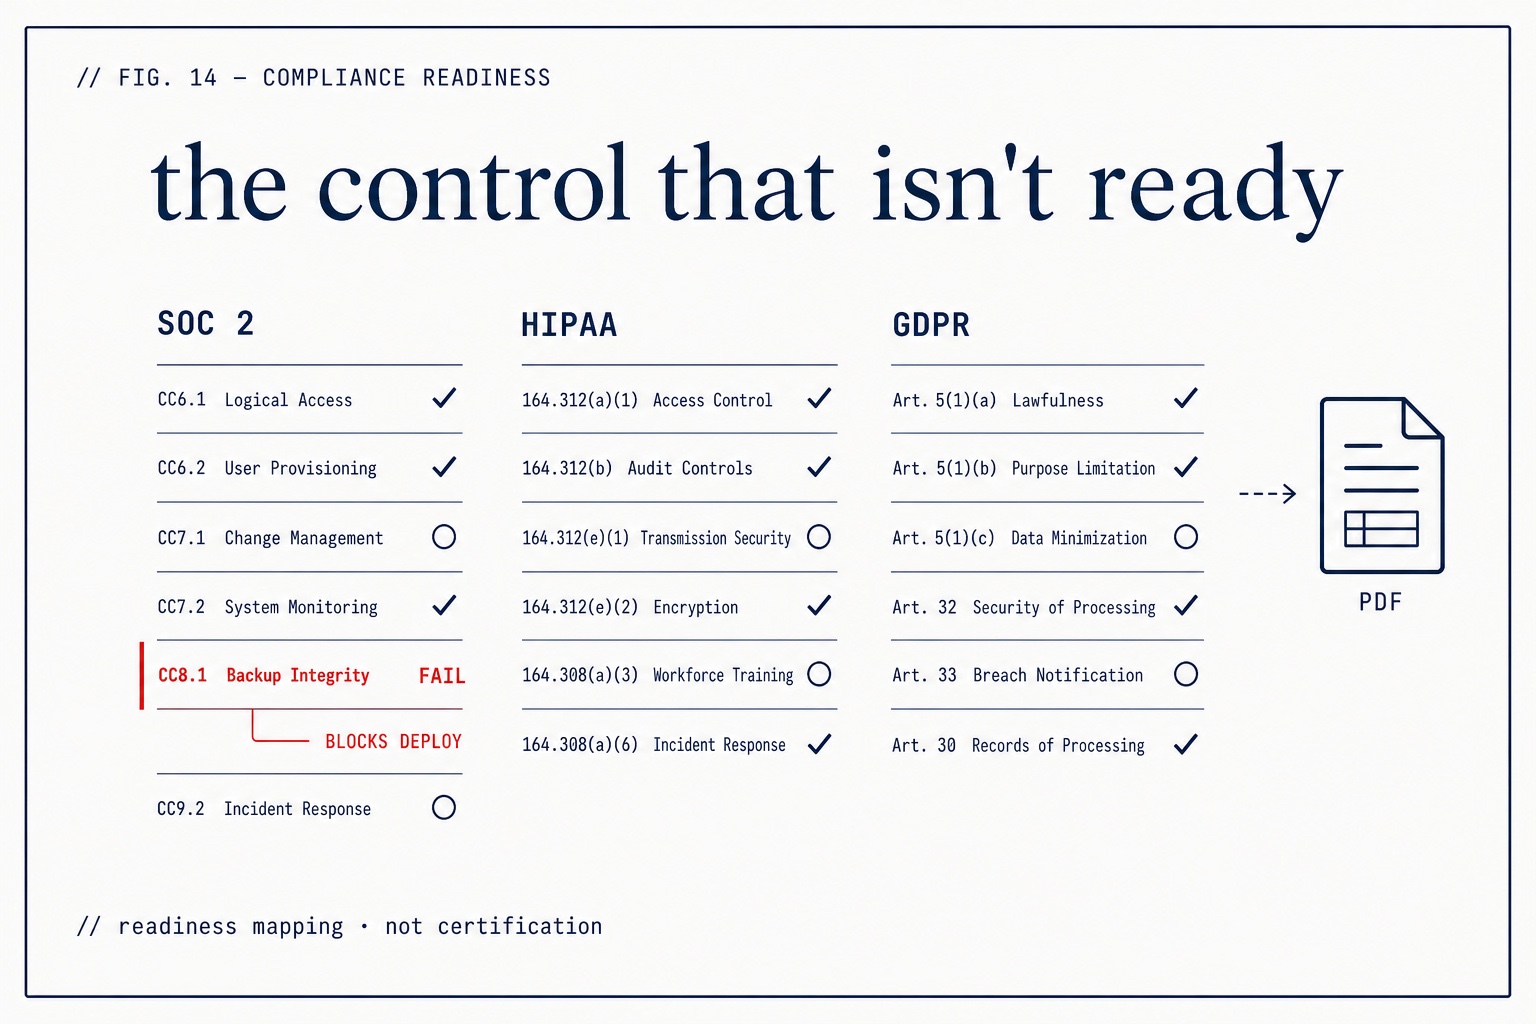
ZipLoom maps SOC 2, HIPAA, and GDPR controls to what it can observe about your project and deployment, marking each control pass, fail, manual, or not-applicable.
A gate, not just a report
Failed blockable controls can stop a deploy before it ships, so a compliance gap is caught at deploy time rather than during an audit.
Downloadable PDF for your auditor
Export the readiness report as a PDF for an auditor or stakeholder. This is a readiness mapping — it is not a certification, and ZipLoom does not claim to certify you or itself.
How readiness mapping works
- 1
ZipLoom evaluates your project against SOC 2, HIPAA, and GDPR control sets.
- 2
Each control is marked pass, fail, manual, or not-applicable.
- 3
Failed blockable controls can gate the deploy.
- 4
You review the readiness report in the Compliance area.
- 5
Export the report as a PDF for auditors or stakeholders.
What this check inspects
Which technical controls you already satisfy — encryption at rest, access control, audit logging, vulnerability management.
Which are partially in place and what specifically is missing.
How each maps to the common framework expectations (SOC 2, ISO 27001) so you can answer questionnaires with evidence.
Where the evidence lives, so you're not reconstructing it the week before an audit.
What it means when this fails
This is a readiness map, not a certification. It tells you honestly which controls a customer's security questionnaire will find in place and which will come back as gaps — before a deal stalls on them.
Questions
- Does this make us SOC 2 compliant?
- No, and be wary of any tool that says it does. Certification requires an independent auditor. This shows which technical controls are genuinely in place and which aren't.
- Do we still need Vanta or Drata?
- If you're pursuing formal certification, yes — those run the full program and cost thousands per year. This covers the technical posture side and is included in your plan.
- Can I share the output with a customer?
- It's built to answer the technical section of a security questionnaire, with the specifics rather than assurances.
What it replaces
Vanta
Compliance automation (SOC 2, ISO 27001). Audit fees are separate. Quote-based.
Drata
Compliance automation; several capabilities are paid add-ons. Quote-based.
Snyk Team
Per contributing developer, 5-seat minimum (~$1,500/yr entry). Code + dependency scanning; does not deploy your app.
ZipLoom Solo — all 28 features included
Deploy, security scan, and monitoring in one flat price. Guild $40/mo · Studio $70/mo · Business $299/mo.
Related features