own
Governed Safety Rules
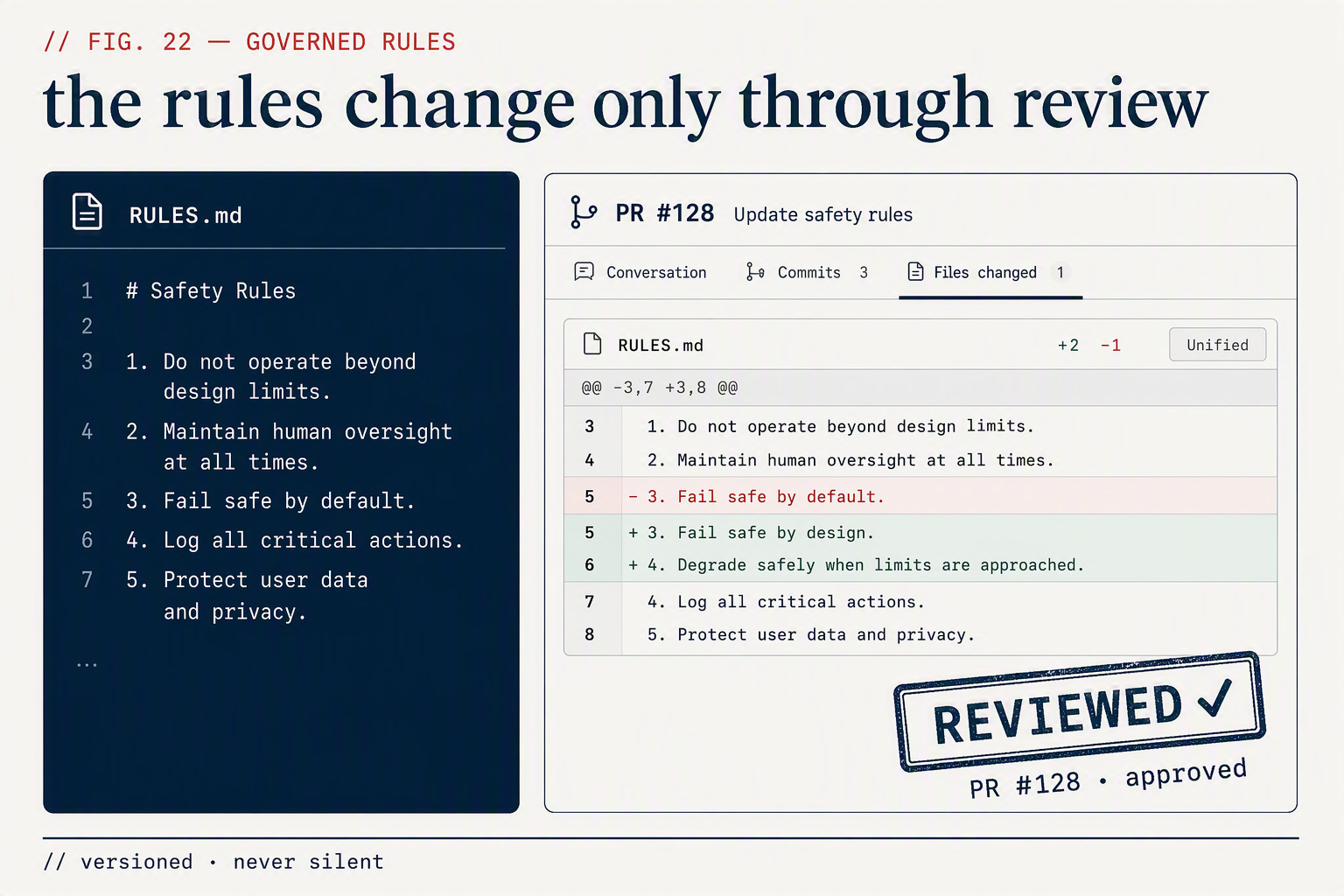
The rules that judge your code are versioned and change only through a reviewed PR.
What you get
Not a black box
You can see exactly what your code is judged against. The safety rules and agent playbooks are files you can read, not opaque logic.
Change only through review
A rule changes only through a reviewed pull request — never silently edited. What decides "safe" is governed the same way your own code is.
Every rule change is attributable
Because the rules ship as reviewed PRs, each change carries an author, a date, and a diff. When a scan result shifts you can point to the exact commit that moved it — not a vendor's silent model update you can neither see nor question.
How governed rules work
- 1
Safety rules and agent playbooks live as versioned files.
- 2
Each rule maps to a live posture check or the code scanner.
- 3
A change to a rule goes through a reviewed pull request.
- 4
The approved version is what your scans are judged against.
What this check inspects
Which rules are active, and what each one checks.
Every change to a rule, as a reviewed pull request with an author and a date.
Which rule produced a given finding, so a result is traceable to a line you can read.
Rule changes that would alter existing results, before they land.
What it means when this fails
If scan results shift and nobody can say why, the tool stops being evidence. Rules shipping as reviewed code means any change in what you're told is attributable to a specific commit — not to a silent vendor-side model update you can neither see nor question.
Questions
- Can I add my own rules?
- Rule changes go through review rather than being edited silently, which is what makes the results defensible.
- Why not just use AI to decide?
- AI is useful for explaining and fixing findings. Deciding whether something is a finding should be inspectable, or you can't defend the result to a customer or an auditor.
- How do I know which rule flagged something?
- Each finding names the rule that produced it.
What it replaces
Semgrep Team
SAST with a strong free OSS engine; rules and triage are yours to maintain.
Snyk Team
Per contributing developer, 5-seat minimum (~$1,500/yr entry). Code + dependency scanning; does not deploy your app.
ZipLoom Solo — all 28 features included
Deploy, security scan, and monitoring in one flat price. Guild $40/mo · Studio $70/mo · Business $299/mo.
Related features