security
AES-256-GCM Secrets Vault
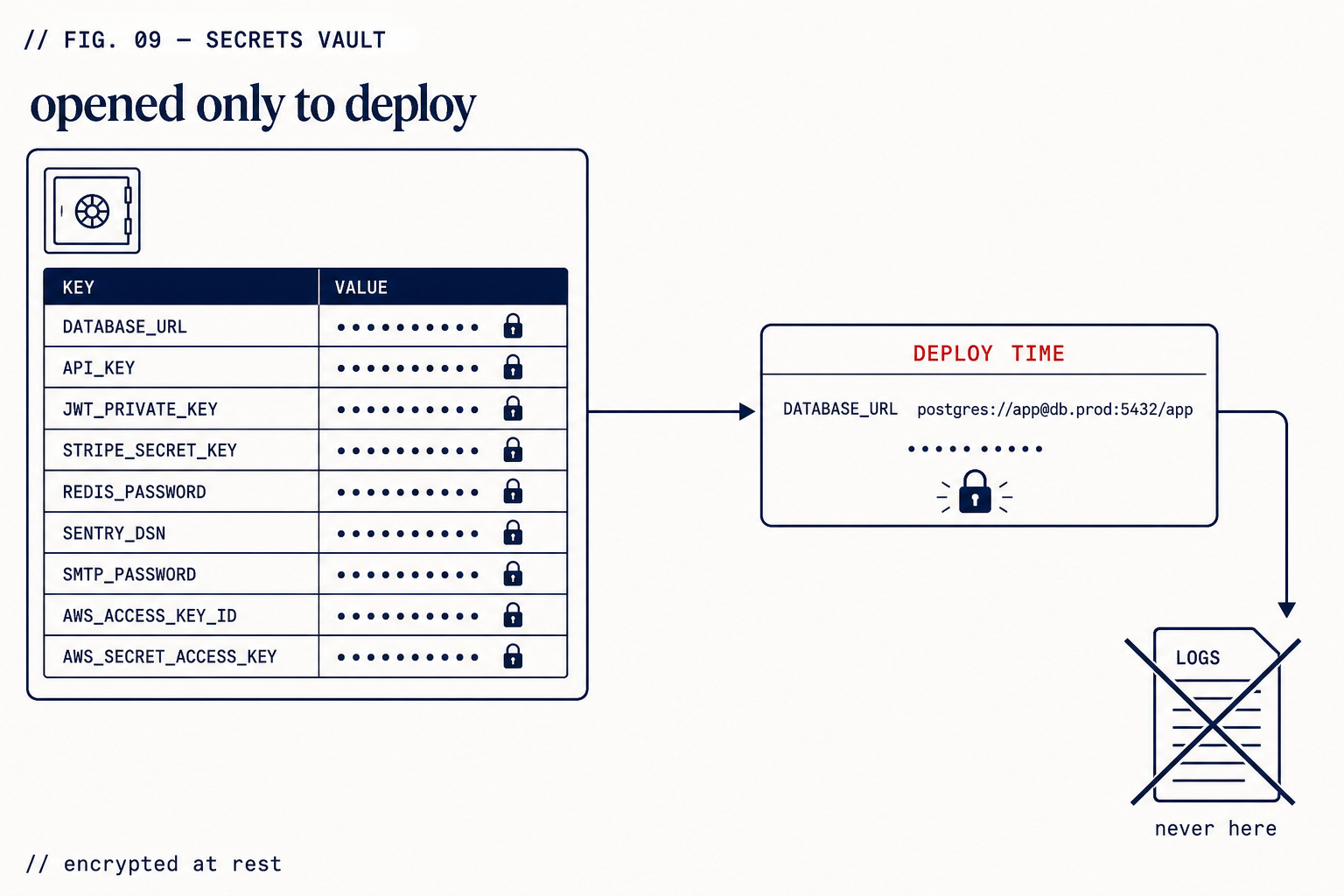
Env vars encrypted at rest — decrypted only at deploy time, never in logs.
What you get
AES-256-GCM encryption at rest
Industry-standard symmetric encryption. Each secret is encrypted with a unique IV (initialization vector) and an authentication tag, making tampering detectable. The encryption key is stored separately from the encrypted data.
Never in logs
Secrets are injected into the build environment at deploy time and scrubbed from any log output. The Stripe key, the database URL, the API credentials — none of them appear in your deploy logs, error reports, or audit trail.
Rotate independently of code
Update a secret in the vault without changing your codebase. The rotation is applied on the next deploy. No git commits, no PR reviews, no change history in your repo for the old credential value.
How it works
- 1
Add your environment variables in Settings → Secrets.
- 2
ZipLoom encrypts each value with AES-256-GCM before writing to the database. The plaintext value is discarded from memory immediately after encryption.
- 3
At deploy time, the build environment receives the decrypted values as standard env vars.
- 4
The decrypted values are never written to disk or included in build logs.
- 5
To rotate a secret, update the value in Settings → Secrets. The old value is overwritten in the vault.
What this check inspects
Every environment variable is encrypted at rest with AES-256-GCM; plaintext never touches the database.
Values are decrypted only at deploy time, for the deploy that needs them.
Access is scoped to your organization and role, and every read and write is written to the audit log.
Values are masked in logs and in the interface, so a screen-share or a build log doesn't leak them.
What it means when this fails
The alternative most AI-built projects fall into is a .env file committed to the repo or pasted into a platform's plaintext settings. Either way the key lives somewhere permanent and readable, and every person who has ever had access still has it.
Questions
- How is this different from my platform's environment variables?
- Most platforms store values you can read back in plain text, and access is tied to the platform account. Here values are encrypted at rest, masked everywhere, role-scoped, and every access is logged.
- Can ZipLoom staff read my secrets?
- They're encrypted at rest and decrypted only in your deploy pipeline. If that's a formal requirement for you, ask us for specifics in writing rather than taking a marketing sentence for it.
- What happens if I leave?
- Self-host export includes your configuration, so you can move without re-keying everything by hand.
What it replaces
Doppler Team
Dedicated secrets manager with SSO, RBAC, and rotation. Free for 3 users; separate from your deploy.
AWS Secrets Manager
Plus $0.05 per 10,000 API calls. Cheap at small scale; AWS-only and wired up by you.
GitHub Secret Protection
Secret scanning and push protection, per active committer. Free on public repos.
ZipLoom Solo — all 28 features included
Deploy, security scan, and monitoring in one flat price. Guild $40/mo · Studio $70/mo · Business $299/mo.
Related features